Lighthouse has a new layout. Prefer the old one? Return to the old layout, and switch back any time from the link at the top of each page.

Exponent CMS 2.6.0 patch2 Stored Cross-Site Scripting (User-Agent)

#1461

Bug description

Exponent CMS 2.6.0 patch2 allows an authenticated user to inject Javascript code on the User-Agent when logging in.
When an administrator user visits the 'User Sessions' tab, the Javascript will be triggered allowing an attacker to compromise the administrator session.

CVSSv3 Vector: CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N

CVSSv3 Base Score: 5.4

Steps to reproduce

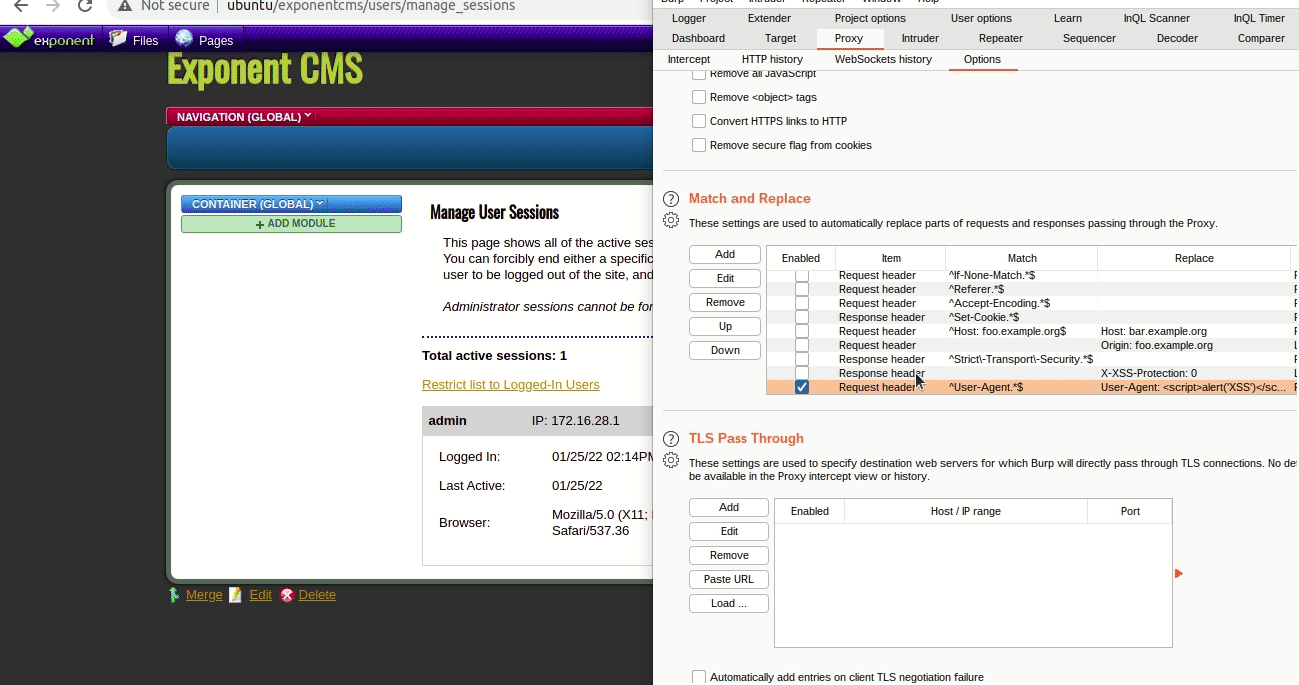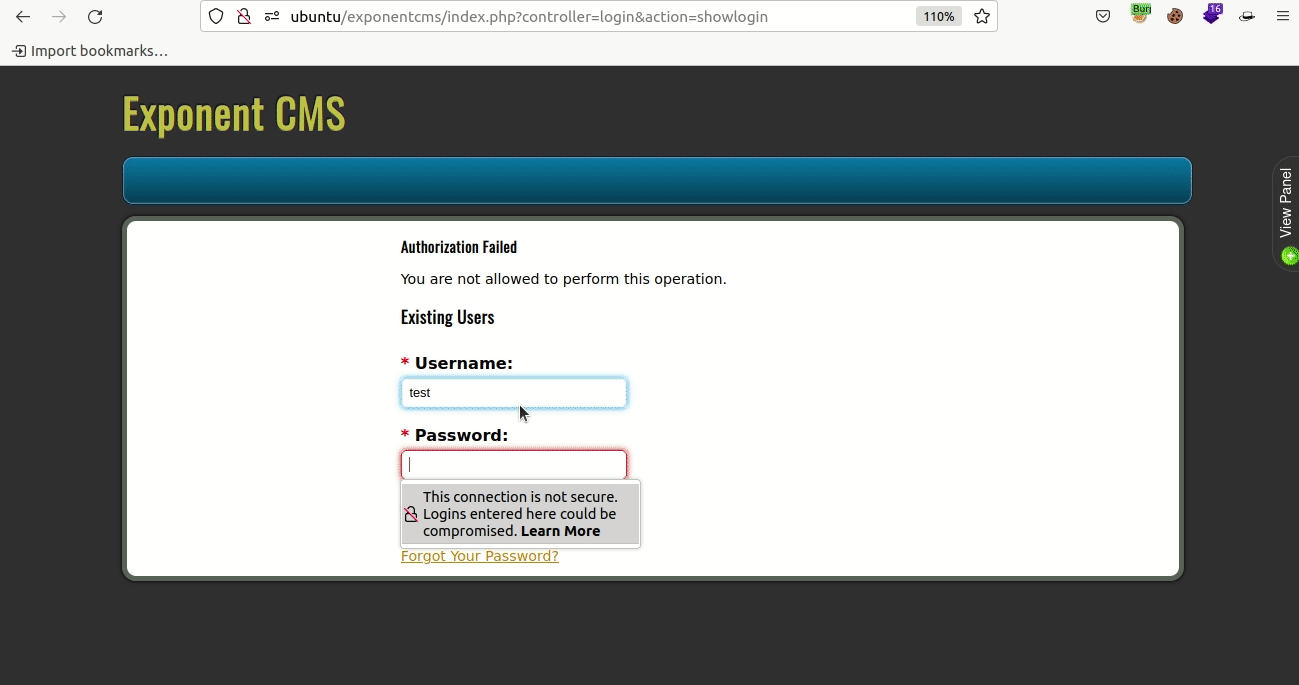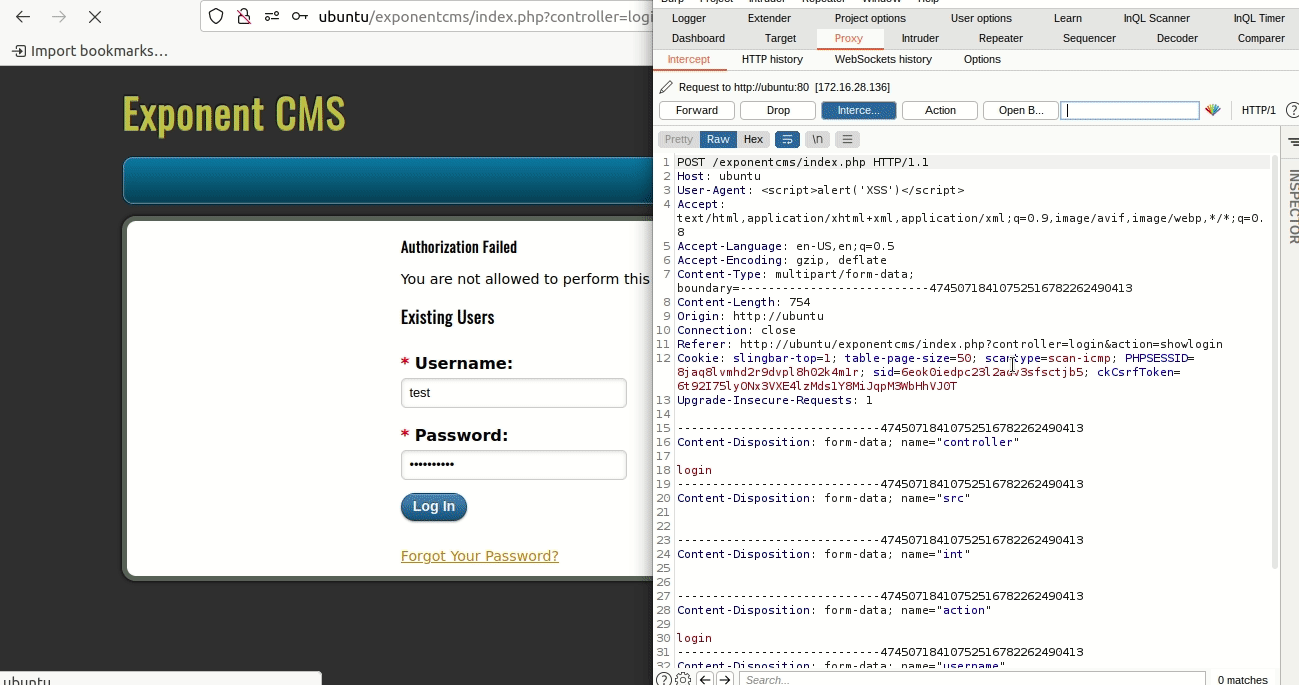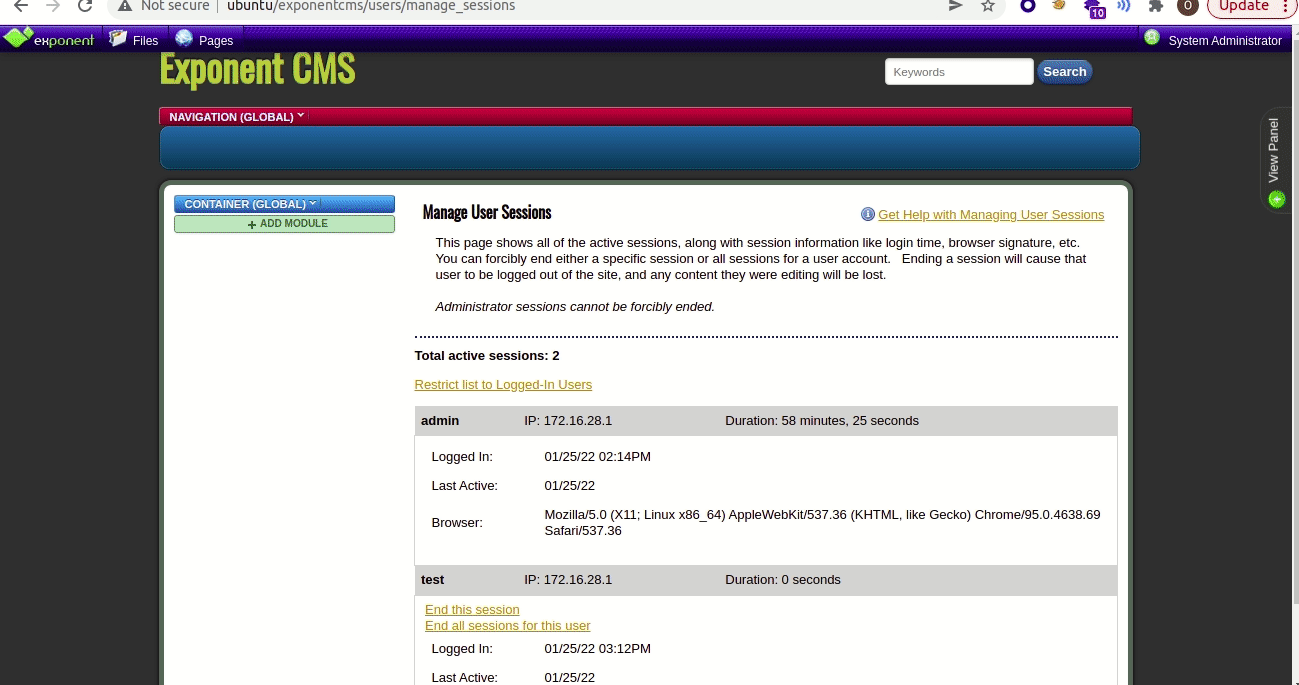
  1. Use a Web proxy or a tool to modify the browser User-agent with the following PoC.
    User-Agent: <script>alert('XSS')</script>
    
  2. Try to login with a non-admin user.
  3. If an admin user visits 'User Management' > 'User Sessions' page, the XSS will be triggered.

Impact

A non-admin user may compromise an admin session by exploiting this vulnerability.

Attached below are the links to the advisory and our responsible disclosure policy.

https://fluidattacks.com/advisories/cobain/
https://fluidattacks.com/advisories/policy

System Information

  • Version: Exponent CMS 2.6.0 patch2.
  • Operating System: Linux.
  • Web Server: Apache
  • PHP Version: 7.4
  • Database and version: Mysql

Reported by Oscar · January 25th, 2022 @ 03:42 PM

State: new
Milestone: none
Assigned to: expNinja expNinja

Activity

Please Sign in or create a free account to add a new ticket.

With your very own profile, you can contribute to projects, track your activity, watch tickets, receive and update tickets through your email and much more.