Exponent CMS 2.6.0 patch2 Stored Cross-Site Scripting Vulnerability
#1459
Bug description
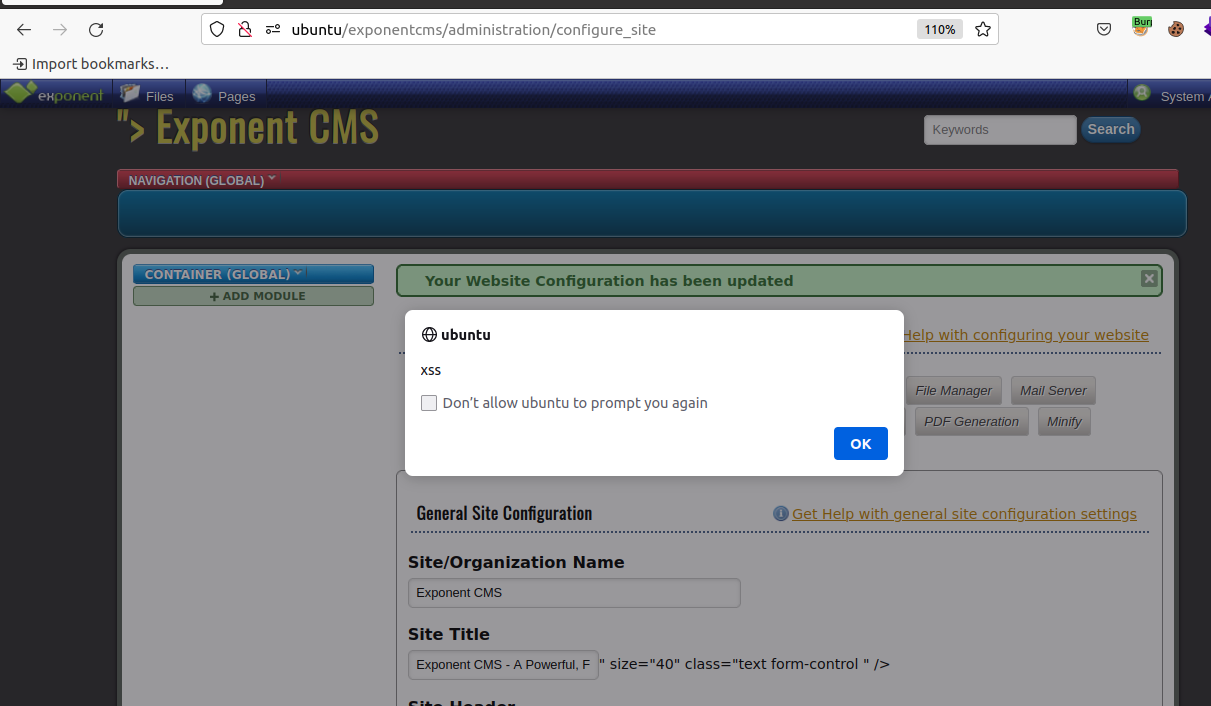
Exponent CMS 2.6.0 patch2 allows an authenticated admin user to inject persistent javascript code inside the "Site/Organization Name,Site Title and Site Header" parameters while updating the site settings on http://127.0.0.1/exponentcms/administration/configure_site.
CVSSv3 Vector: CVSS:3.1/AV:N/AC:L/PR:H/UI:R/S:C/C:L/I:L/A:N
CVSSv3 Base Score: 4.8
Steps to reproduce
- Click on the Exponent logo located on the upper left
corner.
- Go to 'Configure Website'.
- Update the 'Site Title' field (or any of the vulnerable fields
"Site/Organization Name","Site Title" or "Site Header") with the
following PoC.
Exponent CMS" onmouseover=alert('xss')> - If a user hover the mouse over the logo or visits the 'Configure Website' the XSS will be triggered.
Attached below are the links to the advisory and our responsible disclosure policy.
System Information
- Version: Exponent CMS 2.6.0 patch2.
- Operating System: Linux.
- Web Server: Apache
- PHP Version: 7.4
- Database and version: Mysql
-
 xss.png
99.1 KB

Please Sign in or create a free account to add a new ticket.
With your very own profile, you can contribute to projects, track your activity, watch tickets, receive and update tickets through your email and much more.