No HTTP Only Flag Allow An Attacker TO Access Cookies Using XSS Attack
#1236
What is HTTP Only Flag - According To OWASP
If the HttpOnly flag (optional) is included in the HTTP response header, the cookie cannot be accessed through client side script (again if the browser supports this flag). As a result, even if a cross-site scripting (XSS) flaw exists, and a user accidentally accesses a link that exploits this flaw, the browser (primarily Internet Explorer) will not reveal the cookie to a third party.
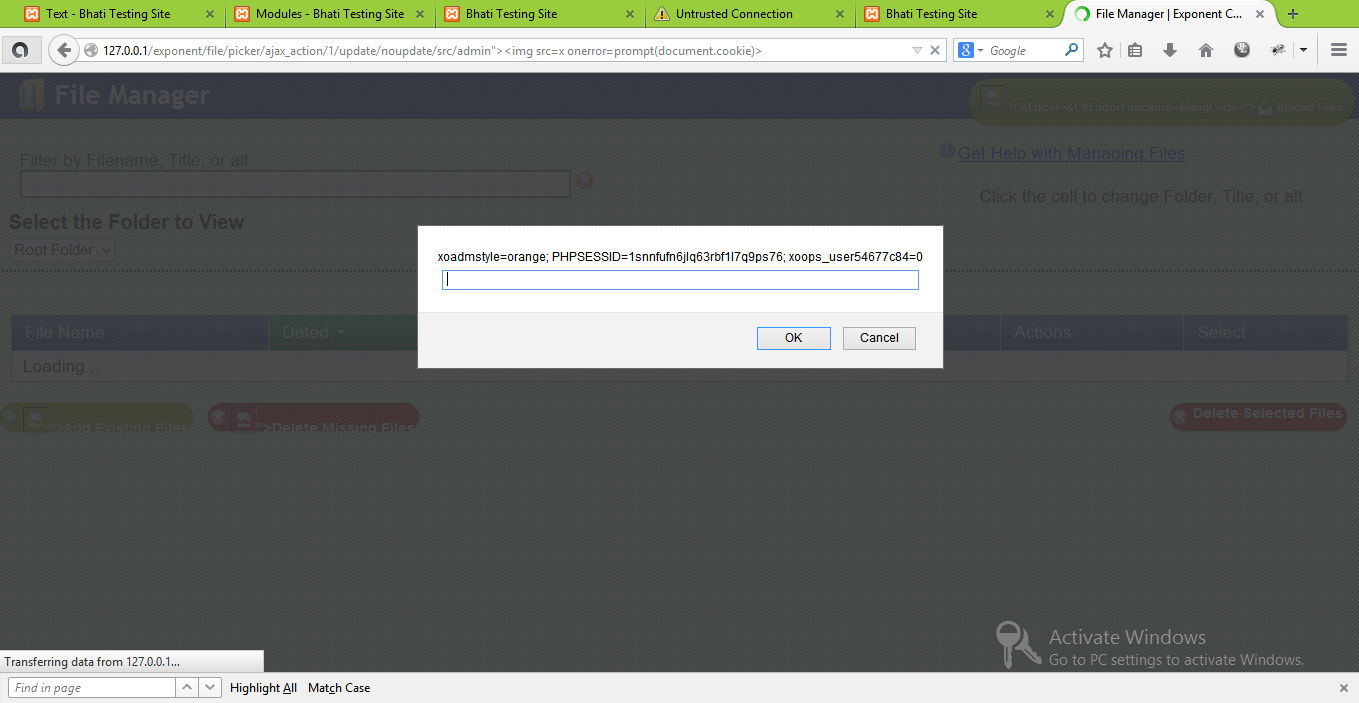
Your cookies are not set as http only flag thats why an attacker can hijack the session cookies by using XSS attack , for further attacks like session hijacking
POC attached with this ticked
-
 Session_Accessable-1.PNG
120 KB

-
 Narendra Bhati
- Tag set to security
-
Narendra Bhati
Any Update ?
-
Please Sign in or create a free account to add a new ticket.
With your very own profile, you can contribute to projects, track your activity, watch tickets, receive and update tickets through your email and much more.