Universal cross-site scripting in Exponent CMS 2.3.1 and prior
Hi,
We found a universal cross-site scripting while testing Exponent
CMS versions prior to 2.3.1. It can be verified by visiting -
http://www.exponentcms.org/news/show/title/time-for-a-heavy-harvest...
http://www.exponentcms.org/news/show/title/%22%3E%3Cscript%3Ealert%...
http://www.exponentcms.org/news/%22%3E%3Cscript%3Ealert%287%29%3C/s...
Seems like Exponent CMS builds the canonical path field from an unsanitized URL, which can be used to execute arbitrary scripts.
Also, another cross-site scripting vulnerability exists in
version 2.3.1 example -
http://localhost/exponent/index.php?int=&src=%22/%3E%3CSCRIPT%3...
Thanks,
Mayuresh Dani (mdani@qualys.com)
Narendra Shinde (nshinde@qualys.com)
-
 Exponent-231.PNG
57.2 KB
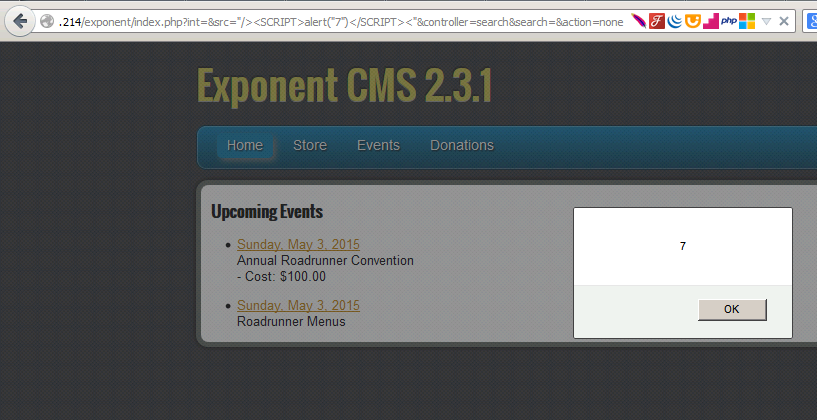

-
 Mayuresh Dani
Also a logged-in user can launch a similar attack simply by entering malicious java script into the "First Name" and "Last Name" fields on http://localhost/exponent/users/edituser. If you enter a simple script tag such as - and you save it, you get the screen shot that I have attached.
Thanks,
Mayuresh and Narendra-
 ExponentUser2.PNG
35.4 KB
-
-
expNinja
(from [f8e878bbe4619c2bcfe4b35ed2fc795e9e384f71]) Better job of scrubbing all params coming in either by sef or query url [#1230 Universal cross-site scripting in Exponent CMS 2.3.1 and prior] https://github.com/exponentcms/exponent-cms/commit/f8e878bbe4619c2b...
-
expNinja
(from [c9a5dc3008834c01f9619215ddeb7ccf1aeefa9a]) More universal/efficient fix for scrubbing parameters [#1230 Universal cross-site scripting in Exponent CMS 2.3.1 and prior] https://github.com/exponentcms/exponent-cms/commit/c9a5dc3008834c01...
-
expNinja
(from [082ab6e21a47940927407cc0bdc10875f5deb3fa]) Better job of scrubbing all params coming in either by sef or query url #1230 Universal cross-site scripting in Exponent CMS 2.3.1 and prior https://github.com/exponentcms/exponent-cms/commit/082ab6e21a479409...
-
expNinja
(from [e18e4d534f5b704954888a8dc9a6a0373fd54247]) More universal/efficient fix for scrubbing parameters #1230 Universal cross-site scripting in Exponent CMS 2.3.1 and prior https://github.com/exponentcms/exponent-cms/commit/e18e4d534f5b7049...
-
Mayuresh Dani
Any updates about the vulnerability in user profiles?
-
Mayuresh Dani
Okay. Would have really appreciated if you guys could have atleast mentioned us for reporting these vulnerabilities when releasing patches though. :-)
-
Mayuresh Dani
Thanks for mentioning us. :-)

Please Sign in or create a free account to add a new ticket.
With your very own profile, you can contribute to projects, track your activity, watch tickets, receive and update tickets through your email and much more.